What's exposed?
Know where critical supplier risk remains.
Continuous third-party cyber assurance
Go beyond supplier questionnaires and cybersecurity ratings.
Identify critical supplier exposures. Drive corrective action. Verify that the risks have been addressed.
Don't just measure supplier cyber risk. Reduce it!
Confidential evaluation for CISOs and security leaders.
Request a walkthroughBusiness outcomes
Know where critical supplier risk remains.
Make remediation ownership accountable.
Distinguish declared completion from verified closure.
The assurance gap
Supplier cyber risk is still largely managed through questionnaires, spreadsheets, certificates, ratings and periodic reviews. But exposure does not wait for the next assessment cycle.
A vulnerability can appear tomorrow. A remediation can remain open for months—or be reported as complete without being technically verified.
CyTrusted is designed to close that gap.
The question is not whether you can find another vulnerability.
Can you prove that critical supplier risks are being identified, acted upon and closed?
The CyTrusted loop
One traceable process connects external signals, supplier action and evidence of closure.
Identify externally observable supplier assets and exposures.
Continuously scan supplier assets with adaptive external attack surface management (EASM), adjusting scope and frequency as risks change.
Combine technical signals with supplier-provided evidence.
Assign, coordinate and track corrective action with suppliers.
Re-test the exposure and confirm the outcome—not the declaration.
Retain a traceable record of findings, decisions and outcomes.
A two-sided model
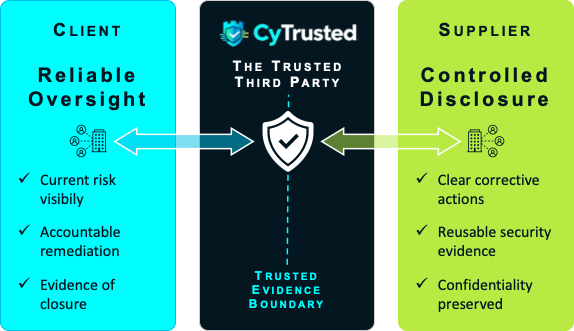
Clients need continuous cyber risk monitoring and remediation assurance to reduce their third-party risk exposure.
Suppliers need a practical way to remediate detected exposures, handle false positives and protect their confidential security information, while reassuring their clients.
CyTrusted acts as a trusted third-party, connecting both sides around shared actions and verifiable outcomes, without requiring suppliers to disclose every underlying document.
NIS2-era supply-chain security
CyTrusted helps security, risk and GRC teams move from periodic supplier checks to ongoing oversight, corrective action and traceable evidence.
Not another annual questionnaire. Not another vulnerability dashboard.
Private access
For enterprises, cybersecurity advisors and managed security providers responsible for critical supplier ecosystems.
Request a private walkthrough